Finally some new stuff (hmm, no)
Let's talk about Win32/Spy.POSCardStealer.O identified by ESET.
It's pretty lame but let's see it anyway.
On the first procedure the malware will register a reg key in HKLM with 'HDebugger'
And start to search for track2:
Then he call the C&C (hoqou.su/forum.php):
• dns: 1 ›› ip: 62.173.149.140 - adresse: HOQOU.SU
Do a sleep of 120000 ms (2 minutes):
And redo into the track2 research procedure.
When finaly something is found the malware took the PID of the program, the process name and the mem adress:
Then he send it to the C&C...
POST req example:
%5BPID%201224%20%28MSR.exe%29%5D%0D%0A%20ADDR%20000B2F90%3A%20%224111111111111111%3D13071010000000000666%22%0D%0A%5BEOF%5D%0D%0A
This malware can't receive orders, and don't have a special mechanism.
On another sample, i've found another domain: rolex216.8s.nl/go/go.php
• dns: 1 ›› ip: 41.223.53.155 - adresse: ROLEX216.8S.NL
This malware was downloaded from a downloader who now download another malware who brute force wordpress sites (maybe i will talk about this one soon).
Still with POS Malware a 'new' threat (Detected only with generic signatures) appeared.
https://www.virustotal.com/fr/file/746cb8cf77b0b00f14c424731948d8fc13378978d193d75f944b12c25e98e0e2/analysis/1376958328/
I got this sample since august from a guys who found this on his POS systems.
In 3 months there is still no one who have do an accurate signature.
At first he will create two directories 'System\Hidden' inside %APPDATA%\Microsoft\Windows
Do a directory test to know from where the executable is launched:
Copy the EXE and launch the copy:
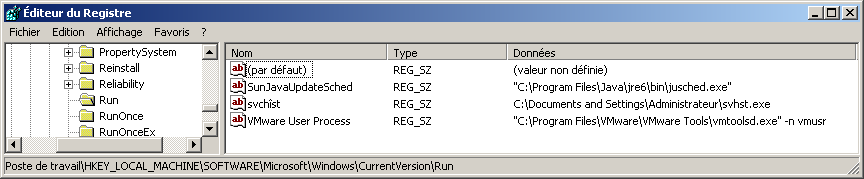
A registry key "Svchost-Windows-Redquired" is created for persistence
Enter in a procedure to remove the original file:
/c del C:\DOCUME~1\ADMINI~1\Bureau\svchost.exe >> NUL
And as excepted send a exit code just after...
So what's do the fresh copy inside the 'good' folder ?
Firstly he take the jump due to the directory test.
On the procedure he will compute a string based on GetSystemFileTime, then he start to enumerate process.
He will open them one by one, read the memory and look for track 2 in a subroutine.
Usual stuff.
They search by partern from the second part of tracks 2 '=13' '=14' '=15' etc..
A file 'Sys.dll' is created:
timestamped with
(encoded)
And wrote:
Do a sleep of 450000 ms (7 1/2 minutes)
if a dump is found the dump is encoded:
And wrote in Sys.dll.
Then they are sent one by one to the C&C:
http://mcsup.cc/8edf4bc26f9c526ff846c9068f387dac/?update=daily&random=563245325050324532495458495358
http://mcsup.cc/8edf4bc26f9c526ff846c9068f387dac/redirect.php
http://mcsup.cc/8edf4bc26f9c526ff846c9068f387dac/website.php
5.9.96.235
The md5 hash '8edf4bc26f9c526ff846c9068f387dac' is 'zabeat'
Showing posts with label sniffer. Show all posts
Wednesday, 4 December 2013
Tuesday, 28 May 2013
Dump Memory Grabber / BlackPOS (Win32/Pocardler.A)
Having a look on another POS malware named by AV guys BlackPOS:
MD5: cbd268e260bf40c25f1bff8b85e04e01
The original exe is packed with UPX and have a size of (292 Kb)
After unpacking the exe size is 754 Kb and the Time/Date Stamp: 512A2914 (24-02-2013 - 14:52:04)
First seen in VirusTotal... right now
This malware retrieve the path of %USERPROFILE%:
At this step we can trick it like ProjectHook to display a leet GUI:
Just take the jump:
Now if we don't take it, it copy the actual file to %USERPROFILE% with the name svhst.exe
execute the original exe with argument '/silentinstall'
I've choose to NOP the line to continue without infecting my vm, and what's he do next ?
The same crap but this time with argument ''/firewall"
Re-NOPed the line and... yeah, you guessed it, still WinExec with "Netsh firewall set opmode disable"
Netsh = network shell, this command will disable the Windows firewall.
Then he delete the file dum.exe (???)
He create after a registry entry: SOFTWARE\Microsoft\Windows\CurrentVersion\Run
RegSetValueExA with 'svchît' as name and %USERPROFILE%/svhst.exe as key.
RegCloseKey:
Now he will load a exe file from ressource:
And file 'dum.exe' is made (the exe file he tryed to delete earlier)
Write it:
And Close when everything is cool:
SetFileAttributesA:
Open it with SW_HIDE:
But what is it new file ?
Yo dawg i herd you like POS malware so we put a POS malware in yo POS malware so you can grab will u grab
MD5: 7f9cdc380eeed16eaab3e48d59f271aa
But if he ShellExecuteA mmon.exe, that mean it swiping time !
So, 'mmon.exe' generate us a file 'output.txt' with our track2. and this 'output.txt' is of course visible.
Meanwhile, BlackPos do a sleep of 400000 ms (6 minutes and 40 seconds) leaving the time for 'mmon.exe' to search track2:
After this sleep, it take output.txt of mmon and try to Create it to see if the file already exist:
Read the content:
Close it:
And create a new text file "03.05.25.txt":
Then he add the content of output.txt inside "03.05.25.txt" and set the file hidden:
Then he connect to FTP (what a good idea!)
.netai.net... maybe he grabbed not enough track2 to buy a decent hosting.
Compare if the domain is equal to localhost:
The he upload the TXT on reports folder and delete dum.exe and output.txt
Then i've stopped here, since i'm at the end of the procedure he surely loop the process of scanning with mmon.
If you want to see what's look like the panel for this sample:
• dns: 1 ›› ip: 31.170.161.116 - adresse: KROKODIL.NETAI.NET
Panel of another sample (d9cc74f36ff173343c6c7e9b4db228cd):
• dns: 1 ›› ip: 31.170.163.50 - adresse: SOBACHKA.COMZE.COM
Old panel of the coder (ree4):
• dns: 1 ›› ip: 109.234.159.254 - adresse: REE4.7CI.RU
The panel is primitive like the malware himself.
Conclusion: /facepalm
MD5: cbd268e260bf40c25f1bff8b85e04e01
The original exe is packed with UPX and have a size of (292 Kb)
After unpacking the exe size is 754 Kb and the Time/Date Stamp: 512A2914 (24-02-2013 - 14:52:04)
First seen in VirusTotal... right now
This malware retrieve the path of %USERPROFILE%:
At this step we can trick it like ProjectHook to display a leet GUI:
Just take the jump:
Now if we don't take it, it copy the actual file to %USERPROFILE% with the name svhst.exe
execute the original exe with argument '/silentinstall'
I've choose to NOP the line to continue without infecting my vm, and what's he do next ?
The same crap but this time with argument ''/firewall"
Re-NOPed the line and... yeah, you guessed it, still WinExec with "Netsh firewall set opmode disable"
Netsh = network shell, this command will disable the Windows firewall.
Then he delete the file dum.exe (???)
He create after a registry entry: SOFTWARE\Microsoft\Windows\CurrentVersion\Run
RegSetValueExA with 'svchît' as name and %USERPROFILE%/svhst.exe as key.
RegCloseKey:
Now he will load a exe file from ressource:
And file 'dum.exe' is made (the exe file he tryed to delete earlier)
Write it:
And Close when everything is cool:
SetFileAttributesA:
Open it with SW_HIDE:
But what is it new file ?
Yo dawg i herd you like POS malware so we put a POS malware in yo POS malware so you can grab will u grab
MD5: 7f9cdc380eeed16eaab3e48d59f271aa
But if he ShellExecuteA mmon.exe, that mean it swiping time !
So, 'mmon.exe' generate us a file 'output.txt' with our track2. and this 'output.txt' is of course visible.
Meanwhile, BlackPos do a sleep of 400000 ms (6 minutes and 40 seconds) leaving the time for 'mmon.exe' to search track2:
After this sleep, it take output.txt of mmon and try to Create it to see if the file already exist:
Read the content:
Close it:
And create a new text file "03.05.25.txt":
Then he add the content of output.txt inside "03.05.25.txt" and set the file hidden:
Then he connect to FTP (what a good idea!)
.netai.net... maybe he grabbed not enough track2 to buy a decent hosting.
Compare if the domain is equal to localhost:
The he upload the TXT on reports folder and delete dum.exe and output.txt
Then i've stopped here, since i'm at the end of the procedure he surely loop the process of scanning with mmon.
If you want to see what's look like the panel for this sample:
• dns: 1 ›› ip: 31.170.161.116 - adresse: KROKODIL.NETAI.NET
Panel of another sample (d9cc74f36ff173343c6c7e9b4db228cd):
• dns: 1 ›› ip: 31.170.163.50 - adresse: SOBACHKA.COMZE.COM
Old panel of the coder (ree4):
• dns: 1 ›› ip: 109.234.159.254 - adresse: REE4.7CI.RU
The panel is primitive like the malware himself.
Conclusion: /facepalm
Subscribe to:
Posts (Atom)