Says hello to another (lame) kit...
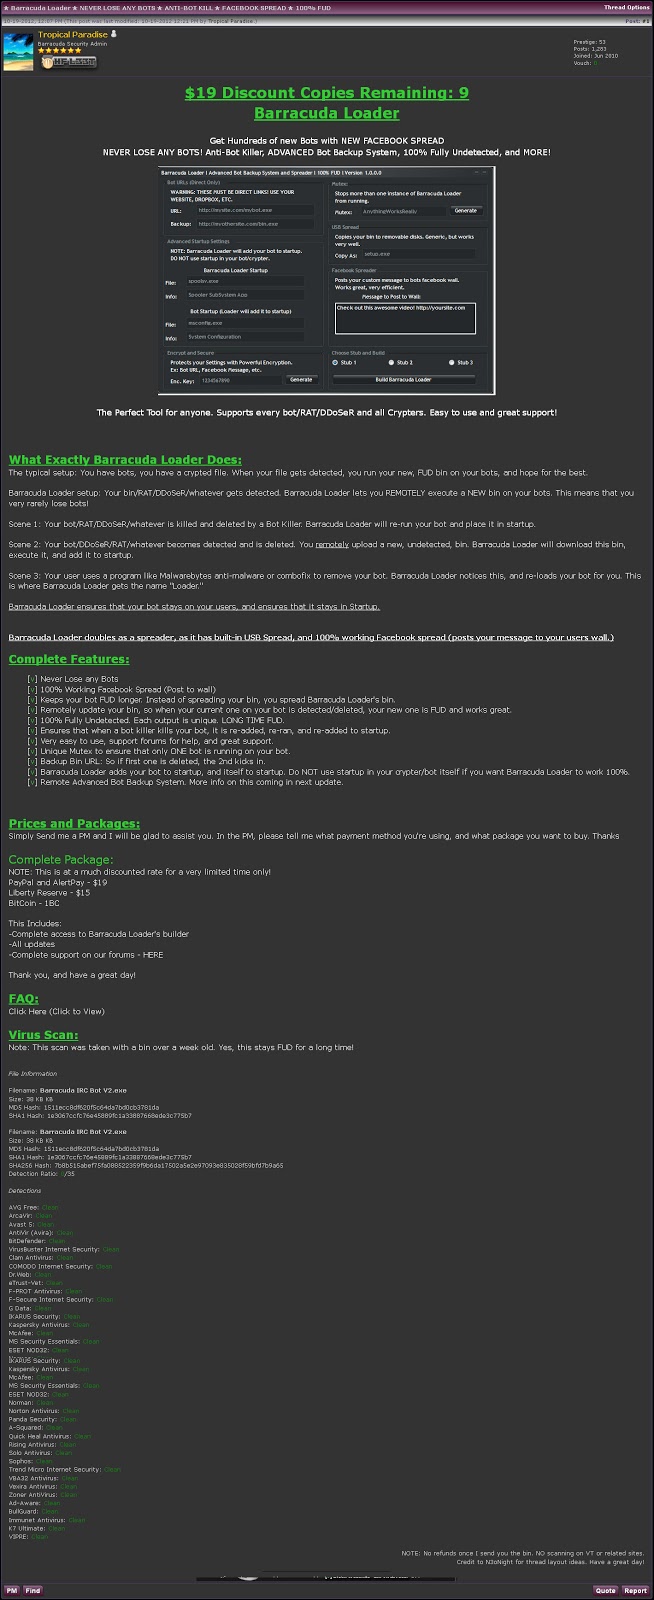
Coded by 'Oakley' the advert look like a HF crap:
We got warned hours later by MDL on Twitter
The kit itself is pretty lame and vulnerable (lol, what an irony), Malekal took some screenshot from the inside with a lame tricks.
http://www.malekal.com/2012/11/16/en-serenity-exploit-pack/
Happy customer:
Quick view of the folders:
• dns: 1 ›› ip: 109.163.231.250 - adresse: WINAMPGROUP.CO.UK
hxxp://winampgroup.co.uk/k0ff/index.php?s=ag
hxxp://winampgroup.co.uk/k0ff/get.php
hxxp://winampgroup.co.uk/k0ff/files/GeoIP.dat
hxxp://winampgroup.co.uk/k0ff/files/cfg.php
hxxp://winampgroup.co.uk/k0ff/files/connectdb.php
hxxp://winampgroup.co.uk/k0ff/files/funcs.php
hxxp://winampgroup.co.uk/k0ff/files/geoip.php
hxxp://winampgroup.co.uk/k0ff/files/heaplib.js
hxxp://winampgroup.co.uk/k0ff/files/js.php
hxxp://winampgroup.co.uk/k0ff/files/load/combo.jar
hxxp://winampgroup.co.uk/k0ff/files/load/ie.html
hxxp://winampgroup.co.uk/k0ff/files/load/ie.php
hxxp://winampgroup.co.uk/k0ff/files/load/ie2.php
hxxp://winampgroup.co.uk/k0ff/files/load/libt.php
hxxp://winampgroup.co.uk/k0ff/files/load/libtiffurl.php
hxxp://winampgroup.co.uk/k0ff/files/load/midi.php
hxxp://winampgroup.co.uk/k0ff/files/load/php_errors.log
hxxp://winampgroup.co.uk/k0ff/files/load/time2.php
hxxp://winampgroup.co.uk/k0ff/files/load/xml.php
hxxp://winampgroup.co.uk/k0ff/files/load/_notes/dwsync.xml
hxxp://winampgroup.co.uk/k0ff/files/s/ag.exe
hxxp://winampgroup.co.uk/k0ff/files/s/default.exe
hxxp://winampgroup.co.uk/k0ff/files/s/st.exe
hxxp://winampgroup.co.uk/k0ff/files/s/_notes/dwsync.xml
hxxp://winampgroup.co.uk/k0ff/spl/chrome.php
hxxp://winampgroup.co.uk/k0ff/spl/ff.php
hxxp://winampgroup.co.uk/k0ff/spl/ie.php
hxxp://winampgroup.co.uk/k0ff/spl/opera.php
hxxp://winampgroup.co.uk/k0ff/spl/safari.php
hxxp://winampgroup.co.uk/k0ff/admin/login.php
hxxp://winampgroup.co.uk/k0ff/admin/links.php
hxxp://winampgroup.co.uk/k0ff/admin/stats.php
hxxp://winampgroup.co.uk/k0ff/admin/checklogin.php
hxxp://winampgroup.co.uk/k0ff/admin/exe.php
hxxp://winampgroup.co.uk/k0ff/admin/filterTable.js
hxxp://winampgroup.co.uk/k0ff/admin/logout.php
hxxp://winampgroup.co.uk/k0ff/admin/images/Serenity.png
hxxp://winampgroup.co.uk/k0ff/admin/images/b-l.png
hxxp://winampgroup.co.uk/k0ff/admin/images/b-r.png
hxxp://winampgroup.co.uk/k0ff/admin/images/bambooimg.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/bg.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/bottom-left.png
hxxp://winampgroup.co.uk/k0ff/admin/images/bottom-right.png
hxxp://winampgroup.co.uk/k0ff/admin/images/dv1.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/dv2.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/dv3.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/footer.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/footer.png
hxxp://winampgroup.co.uk/k0ff/admin/images/header.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/ico_auth.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/ico_cat.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/ico_comment.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/ico_link.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/inp_login.gif
hxxp://winampgroup.co.uk/k0ff/admin/images/left.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/loginbox_bg.png
hxxp://winampgroup.co.uk/k0ff/admin/images/menu1.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/menu2.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/menu3.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/pagebg.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/sidetop.png
hxxp://winampgroup.co.uk/k0ff/admin/images/spacer.gif
hxxp://winampgroup.co.uk/k0ff/admin/images/submit_login.gif
hxxp://winampgroup.co.uk/k0ff/admin/images/t-l.png
hxxp://winampgroup.co.uk/k0ff/admin/images/t-r.png
hxxp://winampgroup.co.uk/k0ff/admin/images/top-left.png
hxxp://winampgroup.co.uk/k0ff/admin/images/top-right.png
hxxp://winampgroup.co.uk/k0ff/admin/images/top.jpg
hxxp://winampgroup.co.uk/k0ff/admin/images/_notes/dwsync.xml
A month ago on the same private forum, a new exploit kit appeared named 'AlphaPack'
Picture:
Even this thread have turned on HF faggotry
(Funny things it's they flame hackforum inside, the admin have even started a thread to make them stop this shit)
As i see from AlphaPack there is Metasploit behind.
When 46.17.102.83/adutaiml/adm/login.php was up i've got a quick view but take no screenshots and shits... sorry guys :)
I've just took note of these folders...
hxxp://46.17.102.83/adutaiml/adm/img/
hxxp://46.17.102.83/adutaiml/adm/css/
hxxp://46.17.102.83/adutaiml/adm/js/
hxxp://46.17.102.83/adutaiml/adm/conf/
hxxp://46.17.102.83/adutaiml/adm/package/
hxxp://46.17.102.83/adutaiml/adm/classes/
hxxp://46.17.102.83/adutaiml/adm/package/alphaPWN/
hxxp://46.17.102.83/adutaiml/exp/data/profiles/1/os/
Kahu Security and others exploit pack guys will probably investigate these new craps better.
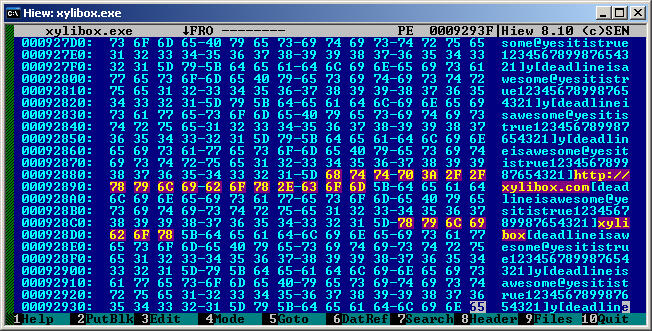
Ah and about the malware loaded on the Serenity Kit, for the love of god.. stop using lame hf crypters who execute the decrypted copy from memory, it's dumpable in two mins.
Edit:
For thoses who wonder what's the payload it's Tofsee.F (a spam and traffic relay)
Unpacked:
Both are on kernelmode.info if you look for files.
And for more info
Unixfreakjp have did investigation on the file:
https://dl.dropbox.com/u/32230830/MalwareMustDie-20121117-01.txt
Looks like they have problem with their urls:
http://host-tracker.com/check_res_ajx/11605033-0/
Edit 2:
http://www.youtube.com/watch?v=2AtB9g5zjsg