Showing posts with label XOR. Show all posts

Thursday, 7 July 2011

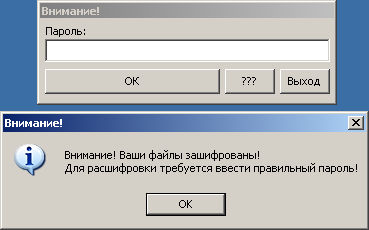
Trojan-Ransom.Win32.Xorist - Encoder Builder v2.31


Another ransomware builder i've found by error (it's true!)

This one is from 2010 and the file encryption used XOR or TEA.
Interesting feature (hm... joke :þ) maybe the number of password attempt who conduct to a melt..


An output have a size of 10,5 Kb and after UPX: 6,5Kb (Builder in Delphi, stub in asm)


https://www.virustotal.com/file-scan/report.html?id=837df40c1667a2369ad9b17537ce5a9efbb81d93917e23426f4bc17fbacb2356-1310063161

The unlock code for decrypts files is not stored in cleartext, but in build MD5x5 hash.
A good solution to recover files without knowing the password... maybe a generic loader for force the good unlock code, it's very weak:


Related ~
Unxoring Trojan-Ransom.Win32.Xorist
WinLocker Builder v0.4 - Cracking Generated winlocks
WinLocker Builder v0.2/v0.3 - Cracking Generated winlocks
xddd.66ghz.com and the 4B XOR Ransomware

Thursday, 2 June 2011

Unxoring Trojan-Ransom.Win32.Xorist


Firstly, thanks to someone, (you know who you are) for the huge pack of samples concerning cryptovirus related to Gpcode :)

Here a simple Xorist, i will not detail it because it's relatively easy to understand the code.
Anyway here is some pics from the debugger

GetDrive and Xor:

Main procedure:

Xoring ~


And drop a txt as usual: Прочти Меня - как расшифровать файлы.txt
Все Ваши файлы были заблокированы!
Чтобы разблокировать Ваш компьютер Вам нужно оплатить 400р. на наш кошелек 41001473616253 в системе яндекс.деньги через любой терминал.
После оплаты скан чека вышлите на email: razblokirovkakompa@gmail.com
После получения нами денег вы получите обратно в течение 24 часов на свой e-mail инструкцию по разблокировке компьютера.
Инструкция по пополнению нашего счета:
http://money.yandex.ru/i/shop/qiwi-instruction.jpg

Также вы можете оплатить любым другим способом, после оплаты в письме на e-mail напишите каким способом вы оплатили и в какое время.

But if it just do a XOR that mean files can be recovered if we open it again :)...
Concerning the file When all files are Xored, it just do an ExitProcess, no autodestruction

Let's open it again.
This time it does an ExitProcess due to a comparison (for avoid a double 'XOR')

When patched and run... you guess it, files are back :)


---------
Some variants who change the wallpaper:


-----------
Videos:


---------
See also ~ xddd.66ghz.com and the 4B XOR Ransomware

Tuesday, 26 April 2011

xddd.66ghz.com and the 4B XOR Ransomware


Another interesting treat today.
A ransomware who XOR the first byte of some formats

If you have your wallpaper changed by this:
You should worry :)
--------------------------

This trojan ransom ( MD5: 359d532274b3a44a8f9bacb942c478d2 ) xor some of your datas.
To recovers your datas, infected users need to payd a ransom (fileunblock@gmail.com - xddd.66ghz.com).

Setup.exe on VT: https://www.virustotal.com/file-scan/report.html?id=5706be5130b214c9885d4098e1b6533c285d9a35c2e923cfed7d73048d12a4e1-1303751832

So how the infection work ?
let's see that.

The infection is composed of two Delphi binary who are exactracted and run by Setup.exe (Setup.exe is a file powered by Smart Install Maker v5.02).
1 File (named svchost.exe) Will crypt your datas and the second (named also svchost.exe) will lock your screen if you attempt something for stop the file

For example if an antivirus is detected or if you browse the website 'VirusTotal' your pc will be locked.
We will see this file later, let's see the one who xor your file.

A file named инфа.txt is created:
все ваши файлы заблокированы посетите сайт: http://xddd.66ghz.com/
вам присвоен id 215 cообщите его на почту указанную на сайте

Infection locs:
%Programs%\Startup\
%ProgramFiles%\KOPPEKTOP\Soft\
C:\ttt.jpg

xddd.66ghz.com Website capture (domain shutdown requested):

---
Firstly the ransomware will crawl these drives:

C:\
D:\
E:\
F:\

In each drive it will list your datas and compare the extention (for know wich files the ransomware will xor)

'Attacked' extentions list:

List:
*.JPG
*.DOC
*.RTF
*.XLS
*.ZIP
*.3GP
*.RAR
*.7Z
*.DOCX
*.MP4
*.PPS
*.DPR
*.POT
*.DOT
*.HTM
*.PDF
*.ISO
*.PPSX
*.EML
*.AVI
*.PPTX
*.HTML
*.TIF

When done, it start to xor all files he have found previously into this loop:

Detail of the procedure:

Take the first byte of your file:

Then it XOR the byte with 4B (41 XOR 0A)
And do a WriteFile for save the change, then it proceed to the next file.

When all files are Xored, it change your wallpaper by 'ttt.jpg' (what a wonderful wallpaper heh...)
0046AF7C=scvhost2.0046AF7C (ASCII "c:\ttt.jpg")
EDX=0012FDBC


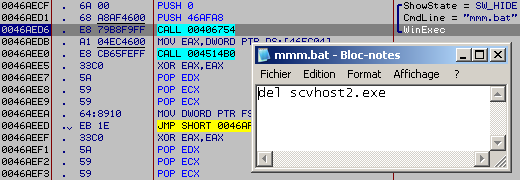
 Then it create a .BAT file for his auto-delete (like that, no proof about the file who xored your datas)


Then ExitProcess (ByeBye)


That all for the first scvhost.exe of 643 Kb.
Now for the second file: the scvhost.exe of 378 Kb

This file is just a protection for the previous one, like i've said
It just do a loop and compare the title of all opened windows

If a windows contain one of these word:

The application will appear maximized on your screen and alway at the top
Tricks like ALT+F4, ALT+TAB, CTRL+ALT+DEL will not work for move the maximized windows.


As you can see here, i've tryed to go on the site 'VirusTotal' and suddenly this grey window appear.
So that all for the second file, just a protection for the real malware.

---------------
How to see your datas back

For the moment i'm really bored to write a asm tool for recover your xored datas (sorry guys) so i'l leave you a pack, a free xor calculator and a free hexadecimal editor, with that you can recover your files manually.

Here you have a header of a JPG, and those who know the header will clearly reconize there is a problem on the first byte:


'B4' here is the first byte of the file, and also a victim of the xor ransomware.
The ransomware XOR all your files with 4B, so do the same operation.
XOR yourself the first byte of your damaged file with 4B
Do that for all your file, the first byte XOR 4B


Here we have the original byte: FF, now save your image and check.


Okay you have some imperfection on the image now, but that not your fault, and the file work again.
Repeat the operation in the files you need.
Click here for download
Archive password: xylibox

Your Antivirus can says calculator.exe is infected due to the wierd packer used but the file is safe ;)
This packaged contain this:


---


Edit 26 Apr 2k11: xddd.66ghz.com is now suspended (:

Monday, 25 April 2011

WinLocker Builder v0.4 - Cracking Generated winlocks


Apparently a new version of Winlocker Builder was released
 VAN32 (the creator) have also released the full Delphi source code.


A generated sample for view the result on VirusTotal: http://www.virustotal.com/file-scan/reanalysis.html?id=2fcf56f7fcdbc267848bbca81fdb83001065cd1bfd137ff285cfb44077d04abe-1303744252

http://www.virustotal.com/file-scan/report.html?id=2fcf56f7fcdbc267848bbca81fdb83001065cd1bfd137ff285cfb44077d04abe-1303744185

Result: 4/41 (9.8%) Dr.Web guys are fast generally for blacklist ransomware threats

On the generated Winlock, the 1024x768 resolution problem seem not yet fixed !

So here we go, what's new on this version ?
A simple homemade XOR on the serial verification.


But one 'lame' thing i've noticed, the xored unlock code is 'unxored' inside and compared in plaintext with the serial entered by the user.
That would have a sens (and more fun to reverse) if the entered serial was xored and compared to the xored unlock code stored inside, but it makes the opposite.


Unlock:


The code source is public, I think we will see soon custom variants.

A simple XOR Reverse done with the original source code of WinLocker Builder v0.4

http://xylitol.free.fr/Reverse%20XOR.zip
Archive password: xylibox

May only the challenge guide you, so don't use this tool. :)

unit Unit1;

interface

uses
  Windows, Messages, SysUtils, Variants, Classes, Graphics, Controls, Forms,
  Dialogs, StdCtrls, XPMan;

type
  TForm1 = class(TForm)
    GroupBox1: TGroupBox;
    Edit1: TEdit;
    Edit2: TEdit;
    Label1: TLabel;
    Label2: TLabel;
    Button1: TButton;
    XPManifest1: TXPManifest;
    procedure Button1Click(Sender: TObject);
  private
    { Private declarations }
  public
    { Public declarations }
  end;

var
  Form1: TForm1;

implementation

{$R *.dfm}

function XOR1(Str: string; Key: string): string;
var
  X, Y: Integer;
  A: Byte;
begin
  Y := 1;
  for X := 1 to Length(Str) do
  begin
    A := (ord(Str[X]) and $0F) xor (ord(Key[Y]) and $0F);
    Str[X] := char((ord(Str[X]) and $F0) + A);
    Inc(Y);
    if Y > length(Key) then Y := 1;
  end;
  Result := Str;
end;

procedure TForm1.Button1Click(Sender: TObject);
begin
  Edit1.Text := XOR1(Edit1.Text, 'asd9sa786ves');
end;

end.

Merci Xash pour le Delphi, ça faisait vraiment longtemps que j'avais pas touché à ça ;)

--------
VAN32 Winlocker Builder on the past ~
Trojan.Ransom (Winlocker builder)
WinLocker Builder v0.2/v0.3 - Cracking Generated winlocks
Trojan.Ransom Private_Brute.exe