They use Security Shield rogue.


Main page

News

Malware download


Redirect

instruction.txt:
Инструкция
----------
1. Создать папку с любым названием
1. Распаковать туда архив redirect.zip
2. Прописать свой урл в конфиг скрипта redirect.php ('url' => 'сюда')
Ссылки брать с раздела Links
3. Установить права на запись в файл link.txt + на папку где он лежит
5. Лить трафик на redirect.php
----------
1. Создать папку с любым названием
1. Распаковать туда архив redirect.zip
2. Прописать свой урл в конфиг скрипта redirect.php ('url' => 'сюда')
Ссылки брать с раздела Links
3. Установить права на запись в файл link.txt + на папку где он лежит
5. Лить трафик на redirect.php
Statistics

Account info

Payement

Contact

Some crap with PECompact 2


Event test
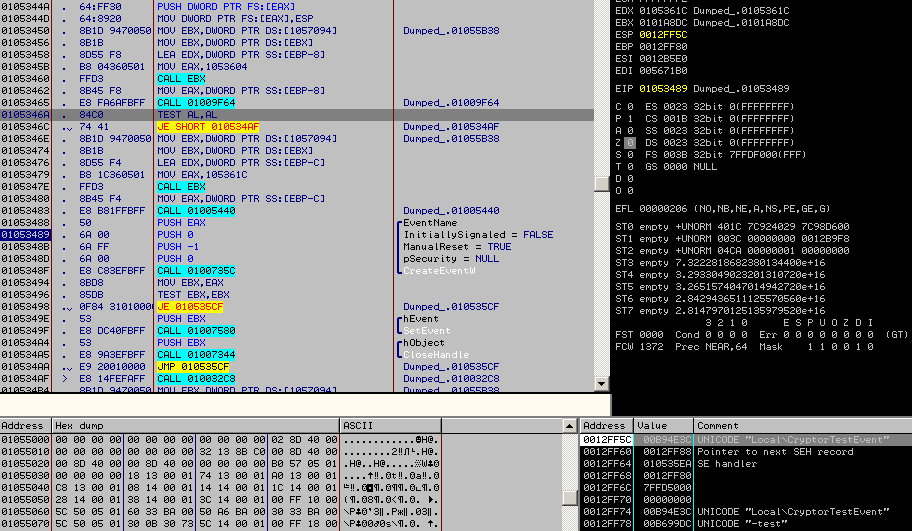
"I'm here"

Infection dropped into
C:\Documents and Settings\(user)\Local Settings\Application Data


Anti vm/sandbox, usual stuff..
Following IP's was identified.
91.223.89.100
31.44.184.62
31.44.184.62
The distribution system seem also got links with Bitcoin mining botnet
[91.223.89.100]
91.223.89.99/loader2.exe
91.223.89.99/loader20_lite.exe
91.223.89.99/ddhttp.exe
91.223.89.99/loader2.exe
91.223.89.99/loader20_lite.exe
91.223.89.99/ddhttp.exe
Edit 09 Sep:
Domain changed:
Statistic temporarily disabled:

